Human
People and workforce identities, with authentication, authorization, lifecycle and governance.
PrincipalFrame is an independent research and engineering project exploring how identities, permissions, delegation and privileged access should work across modern enterprise systems.
Modern systems involve different types of principals, from people to workloads to autonomous agents. Each requires authentication, authorization and governance. PrincipalFrame examines both the principals and the control frame that governs them.
People and workforce identities, with authentication, authorization, lifecycle and governance.
Service accounts, workloads, applications and non-human identities.
Agents that can reason, delegate and act across systems, with independent access and permissions.
The controls, policies and governance that define how principals are authenticated, authorized, delegated to, monitored and held accountable throughout their lifecycle.
PrincipalFrame publishes technical research, develops architectural frameworks and produces practical engineering tools addressing identity, authorization and governance across different principal types.
Analysis of emerging identity, authorization and privileged-access problems, with an emphasis on architecture and implementation.
Explore Research →Reference architectures, models and control frameworks for human, machine and autonomous identities.
Explore Frameworks →Assessment sheets, checklists, scripts and engineering utilities intended for practical use.
Explore Tools →Governing purpose and intent across human, service, workload and agent principals.
The 4A Control Model examines Authentication, Authorization, Alignment and Accountability across human, service, workload and agent principals.
Read the research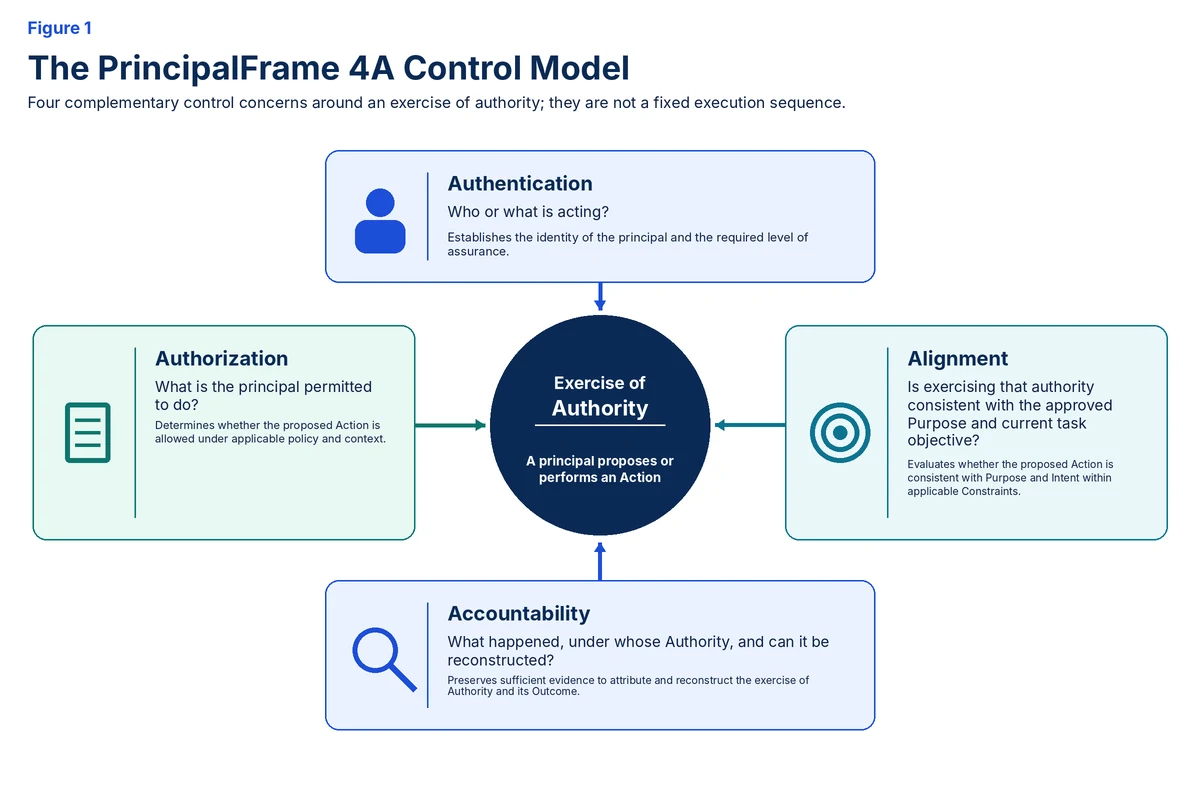 Figure 1. The PrincipalFrame 4A Control Model